AI-powered scams
Cloned voices and scripted chats make every scam sound real.
We can’t hear the call. We see what it does to the phone: remote access, a guided session, a new device.
See the threatPatent published in India, grant awaited.
Your customers keep their money. Your team stops firefighting fraud cases. Your business stays out of the news — because the fraud is caught before the money moves.
We help you meet the mobile cybersecurity, digital payment and RASP requirements in these regulations
Requirements as set out in each published regulation or standard. Not an endorsement or certification by these bodies.
No more juggling multiple security tools. NonaShield is one unified platform that protects your mobile app end to end, from the first launch to the final transaction.
* Illustrative annual total cost of ownership for a mid-size app: compared with running five separate point tools. Actual costs vary.
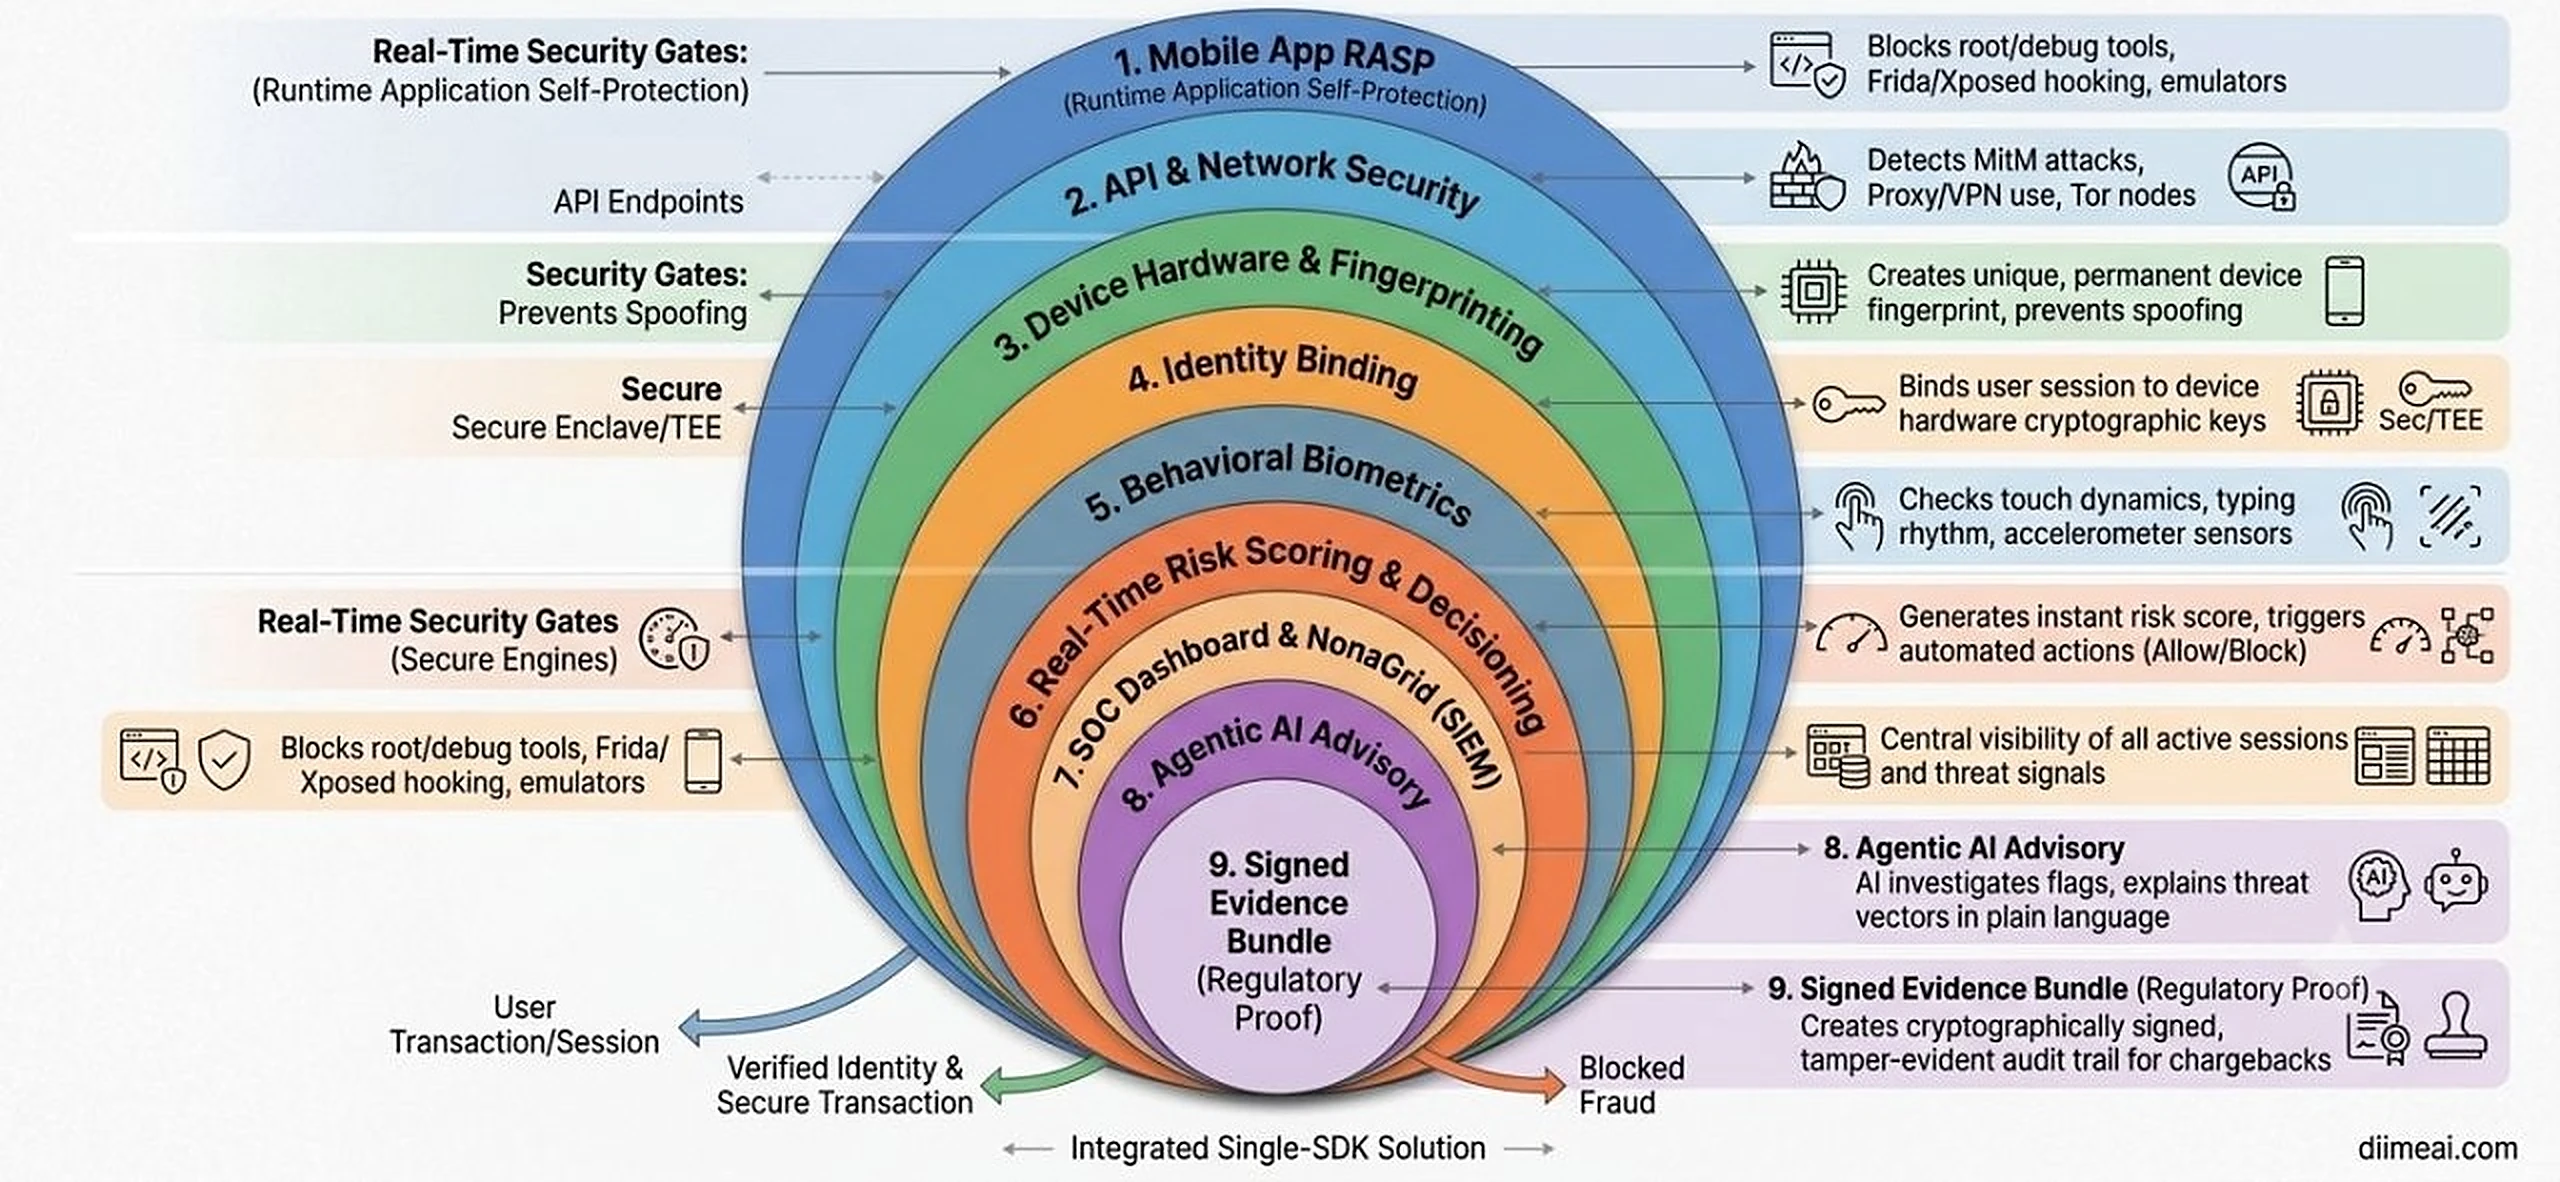
Mobile app, device hardware, identity, behaviour, network traffic, risk decisions, an AI investigator and the dashboard that watches it all — stacked here in the order they actually work together.
Hover or tap a layer to see what it does and which fraud it helps stop. Or scroll down to walk through each layer in order.
Your App, Watched From Inside.
Continuously monitors the mobile app at runtime and detects hostile environments, instrumentation and application manipulation.
Every Request, Verified.
Attackers can intercept or manipulate mobile-to-API communication using MITM attacks, proxies, VPNs, Tor, replay and network manipulation. Signed-payload checks and replay protection at the edge, so a forged, altered or replayed request is rejected before it reaches your backend.
A Device That Proves Itself.
A cryptographic key that never leaves the device's secure hardware proves it's genuine and untampered — then signs every transaction it approves.
Confirms It's Really You.
Binds the transaction to the enrolled user on their own device, so a stolen session or spoofed identity doesn't pass as the real customer.
Knows How You Normally Use Your Phone.
Baselines typing rhythm, motion and everyday usage patterns to catch a fraudster — or a scammer talking a real customer through a transfer.
A Verdict, in Real Time.
Every transaction gets an instant decision — allow, step up, or block — before the money moves.
Your Own Security Command Center.
Live monitoring inside your own cloud account — one dashboard instead of stitching together a separate SIEM.
An Analyst for Every Case.
Investigates every flagged transaction and explains the decision in plain language — no black box, no guessing.
Create Forensically Defensible Evidence.
Creates a "cryptographically signed, tamper-evident evidence bundle" containing relevant security events, decisions, timestamps and control results. Mapped to regulatory compliance.
One Platform. Nine Layers. Every layer that can touch a transaction — app, device, identity, network, behaviour and the humans who review it — working together under one SDK, one console, one vendor.
Don't spend months integrating bulky infrastructure. Our turnkey threat architecture deploys complete command, telemetry, and automated mitigation straight into your environment within a single day.
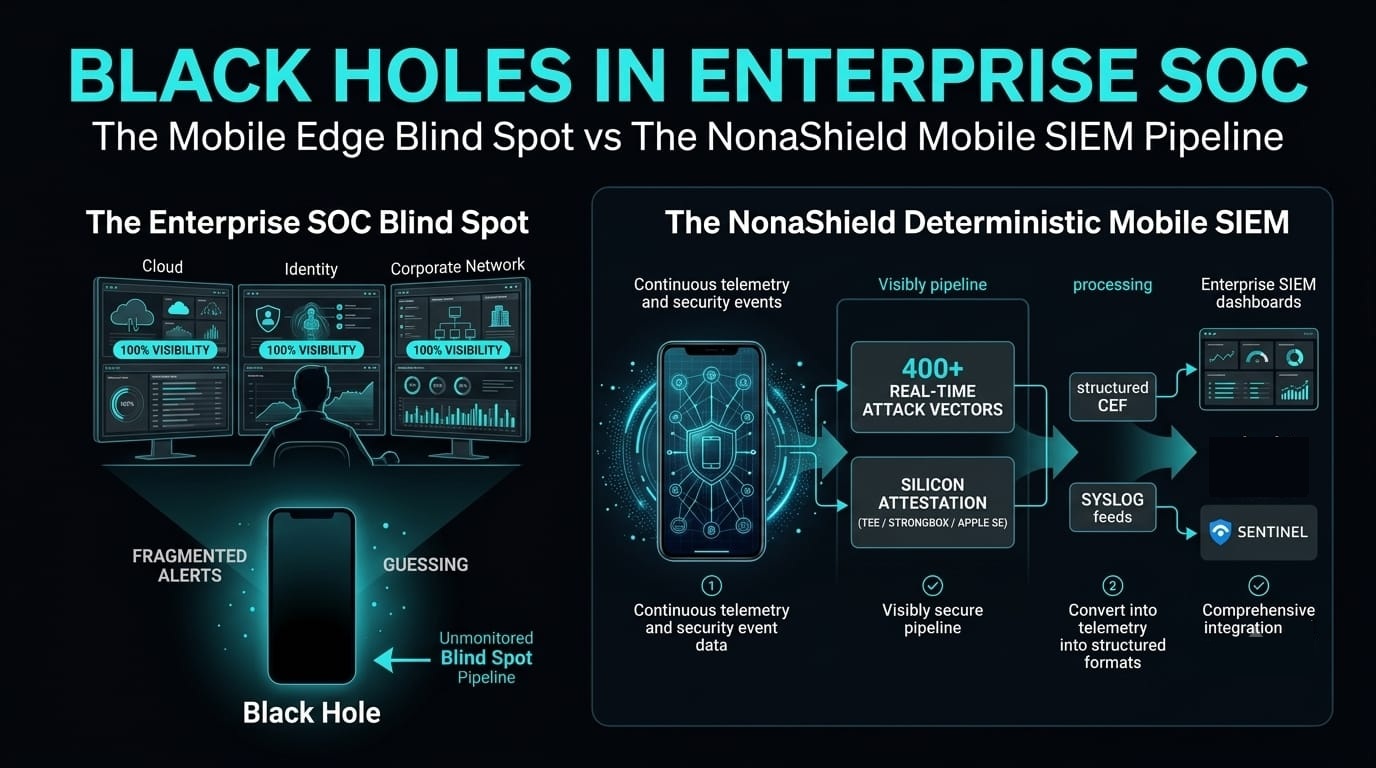
Simulated events for illustration. Not customer data.
Every transaction gets a signed, tamper-evident record. When a customer disputes a charge, or a regulator asks for proof, you have a real answer ready — not a guess.
It also supports India's newest data-safety law.
DPDP Rule 6 requires reasonable security safeguards on personal data. NonaShield's evidence and access controls map to it.
See the Full Compliance Mapping →The money moved to one device. The controls did not move with it.
A single fraud case means hours of investigation, an upset customer, a regulator asking questions, and your team pulled off real work to piece together what happened. Multiply that by every case your app doesn't catch, and "a few fraud incidents a month" quietly becomes a full-time operational problem.
Sources: Neontri, Mobile Banking Statistics 2026 (global figures are market projections) · NPCI / PIB, UPI at 10 Years, 2026.
Almost none of it is a broken phone.
Sources: Juniper Research, Online Payment Fraud Losses report · BioCatch, India Digital Banking Fraud Report, Jul 2026 · Ministry of Finance, India, Rajya Sabha (Internet Banking, Credit Card and UPI fraud combined, FY22–Sep 2025).
Answer one — what you have watches the phone. The fraud never touched the phone. Every one of these happened on a handset that passed its security check.
Cloned voices and scripted chats make every scam sound real.
We can’t hear the call. We see what it does to the phone: remote access, a guided session, a new device.
See the threatA relay turns the victim’s phone into the fraudster’s card reader.
Flags rogue payment handlers and known relay tools on Android.
See the threatA fake officer, a video call that never ends, and a customer who transfers everything.
Sees a video call and a payment at the same time, with an amount far above normal. We don’t listen to the call.
See the threatWhen a customer is defrauded, the RBI’s customer-liability rules can leave the bank carrying the loss.
A signed, tamper-evident record of what the device, app and session looked like shows what really happened.
See the evidenceFrom 13 May 2027, if a customer says they never agreed, the burden of proof is yours.
DPDP Consent Manager keeps signed, tamper-evident records that anyone can verify.
See howWhat each scam looks like on the phone, and what NonaShield sees. Your policy decides the response: step-up, review or block.
Cloned voices, fake video calls and scripted chats make scams more convincing and let them scale.
NonaShield cannot hear the call, but it sees the effect on the phone: remote-access tools, a hesitant, guided session, a new device or an impossible location.
A relay app forwards a victim's tap-to-pay to a fraudster's reader.
A rogue default payment handler or a known relay tool is present on the device.
A fake officer keeps the victim on a video call and orders transfers to “clear their name”.
A video call and a banking session at the same time, repeated high-value transfers, an amount far above the customer's normal. NonaShield does not listen to or record the call.
The victim is tricked into merging calls, and the fraudster hears the one-time password as it arrives.
A VoIP call and a cellular call active together, with an OTP requested during the call.
A caller talks the customer into installing a remote-access app, then steers a real payment from the customer's own phone.
Detects remote-access tools, screen mirroring and overlays on the device, and reads the session's behaviour to spot a guided customer.
Stolen credentials, a hijacked session or a captured one-time password are used to log in as the real customer.
Binds each transaction to the enrolled customer's own device with a key held in secure hardware, so a stolen session or password alone does not pass as the real customer.
Malware watches the banking app, draws fake screens over it, or abuses accessibility services to read and tap.
Runtime protection watches the app from the inside, detects hooking, overlays and tampering, and responds on the device.
One attacker runs copies of the app, or virtual phones, to create many fake users at scale.
A hardware-attested device fingerprint recognises the same device across accounts, so one handset behind many accounts shows up as a ring instead of ten clean logins.
The fraudster moves the victim's number to a new SIM to receive one-time passwords and reset access.
A new SIM alone does not make a new device trusted. A change of device or network triggers a step-up check, and the hardware key stays with the enrolled phone.
A “KYC update” or “rewards” APK arrives in a chat, and the customer installs it.
An app installed from a messaging app instead of the store, or one holding device-admin rights that block uninstalling.
Predatory loan apps harvest contacts, SMS and call logs to harass borrowers and their families.
A non-banking app holding contacts, SMS and call-log access is flagged as a risk signal.
Scripts and device farms open accounts in bulk to run mule networks.
Many sign-ups from one device in minutes, no motion-sensor activity, paste-only forms and scripted touch.
Run NonaShield on your own traffic and see which of these your current stack misses. Free 7-day trial, no card.
Start the free trialPlatform labels show where the main signal runs today.
One SDK in your app. Four checks on every session. A decision in real time, and proof of it afterwards.
Catches rooted and hooked devices, emulators, tampered apps and screen-sharing.
Recognises the same device across accounts, so mule rings and repeat fraud stand out.
A key locked in the phone’s secure hardware ties each customer to their own genuine device.
Touch, typing rhythm and motion build a “how this person acts” profile. Sudden changes raise the risk.
Your policy, your thresholds. Every decision is signed and recorded, ready the moment anyone asks what happened.
Android, iOS and React Native: one SDK, one managed platform.
Our SaaS cloud, your own VPC, or fully on-premise. With the last two, your data never leaves your environment.
A live dashboard maps controls to RBI, NPCI, PCI DSS and DPDP requirements, and other frameworks. See the full mapping
400+ threats and vulnerability checks, 300+ mapped to compliance clauses, live. No new hardware. No extra steps for your customers.
Start the free 7-day trialEvery consent and every withdrawal becomes a signed record that you hold and anyone can check offline. When a customer, an auditor or the Board asks what was agreed, you show the record, not a screenshot.
The DPDP Act applies to every business that collects personal data in India, not only banks. The consent duties apply in full from 13 May 2027, so the time to build the record is now.
Every transaction decision rests on two questions. Identity: is this the enrolled customer on their own device? Location: is the session where it claims to be? Fraudsters attack both, with cloned devices, stolen sessions, spoofed GPS, VPNs and proxies.
Keys created in secure hardware tie each customer to a genuine device that cannot be cloned.
How hardware-bound identity works →Impossible-travel speed, GPS-versus-IP checks and a learned home zone expose spoofed locations.
See the location checks →*Sample data
These cards are reading your own browser's signals live — the same device-trust checks our web agent runs, including whether this device has a real hardware-backed authenticator.
Hello, Visitor
Reading signals…
Browser
—
Screen
—
Timezone
—
Hardware Auth
—
This Is Real Data
Trust Signal
Reading…
Computed from the signals on the left — automation, DevTools, and hardware-authenticator checks.
Uses your browser's own location permission — nothing is stored.
Start with the full platform, or buy the single product you need.
The full system — one setup covers every layer of protection.
Pick what you need. Try any of them free, then decide.
Runtime protection, device fingerprint, hardware-bound identity, behaviour signals, fraud engine and evidence — one setup.
Start Free TrialConsent Manager for Data Fiduciaries. Start with a 7-day free trial.
Start Free Trial* $599 does not include Agentic AI Advisory.
NonaShield is a mobile fraud and device-trust platform from DIMEAI. One SDK adds runtime protection, device fingerprinting, hardware-bound identity, behavioural risk scoring and signed evidence to a banking, lending, trading or payment app.
It is one unified platform instead of several tools. Mobile RASP, device fingerprinting, identity, behaviour and risk scoring share the same signals and the same dashboard, so a decision uses everything the platform knows.
NonaShield is priced at a flat $599 a month and includes RASP, fingerprinting, identity and evidence. See the pricing page for what is included.
It helps mobile apps meet published requirements from RBI, NPCI, SEBI and DPDP, and supports PCI DSS controls for mobile payment applications. It is not an endorsement or certification by those bodies.
Sign up with your company email and choose the free trial or a monthly plan. We'll send a verification link first. The trial needs no card.
General
contactus@diimeai.comDirect Engineering
jrajesh@diimeai.comWhatsApp Business
+91-8591-755-427If that looks right, we've sent a verification link to your company email. Click it to confirm your request — our team then sends your trial SDK, SDK key and integration guide. Your 7 days start the day we send them.