Patent-Backed. Built to Be the First of Its Kind.

Stop the Fraudster,
Before the Fraud.

Your customers keep their money. Your team stops firefighting fraud cases. Your business stays out of the news — because the fraud never got through in the first place.

RBI-Mapped Controls
DPDP Rule 6 Ready
Watch: How NonaShield Works
NonaShield
Device → App → Identity → Transaction

We help you meet the mobile cybersecurity, digital payment and RASP requirements in these regulations

  • RBIDigital payment security controls
  • NPCIUPI mobile app security and RASP
  • SEBICSCRF mobile app security
  • PCI DSSMobile payment application controls
  • DPDPDigital personal data protection
  • RBIDigital payment security controls
  • NPCIUPI mobile app security and RASP
  • SEBICSCRF mobile app security
  • PCI DSSMobile payment application controls
  • DPDPDigital personal data protection

Requirements as set out in each published regulation or standard. Not an endorsement or certification by these bodies.

The NonaShield Mobile Solution

One Simple Mobile Setup.
Protection Everywhere.

No more juggling multiple security tools. NonaShield is one unified platform that protects your mobile app end to end, from the first launch to the final transaction.

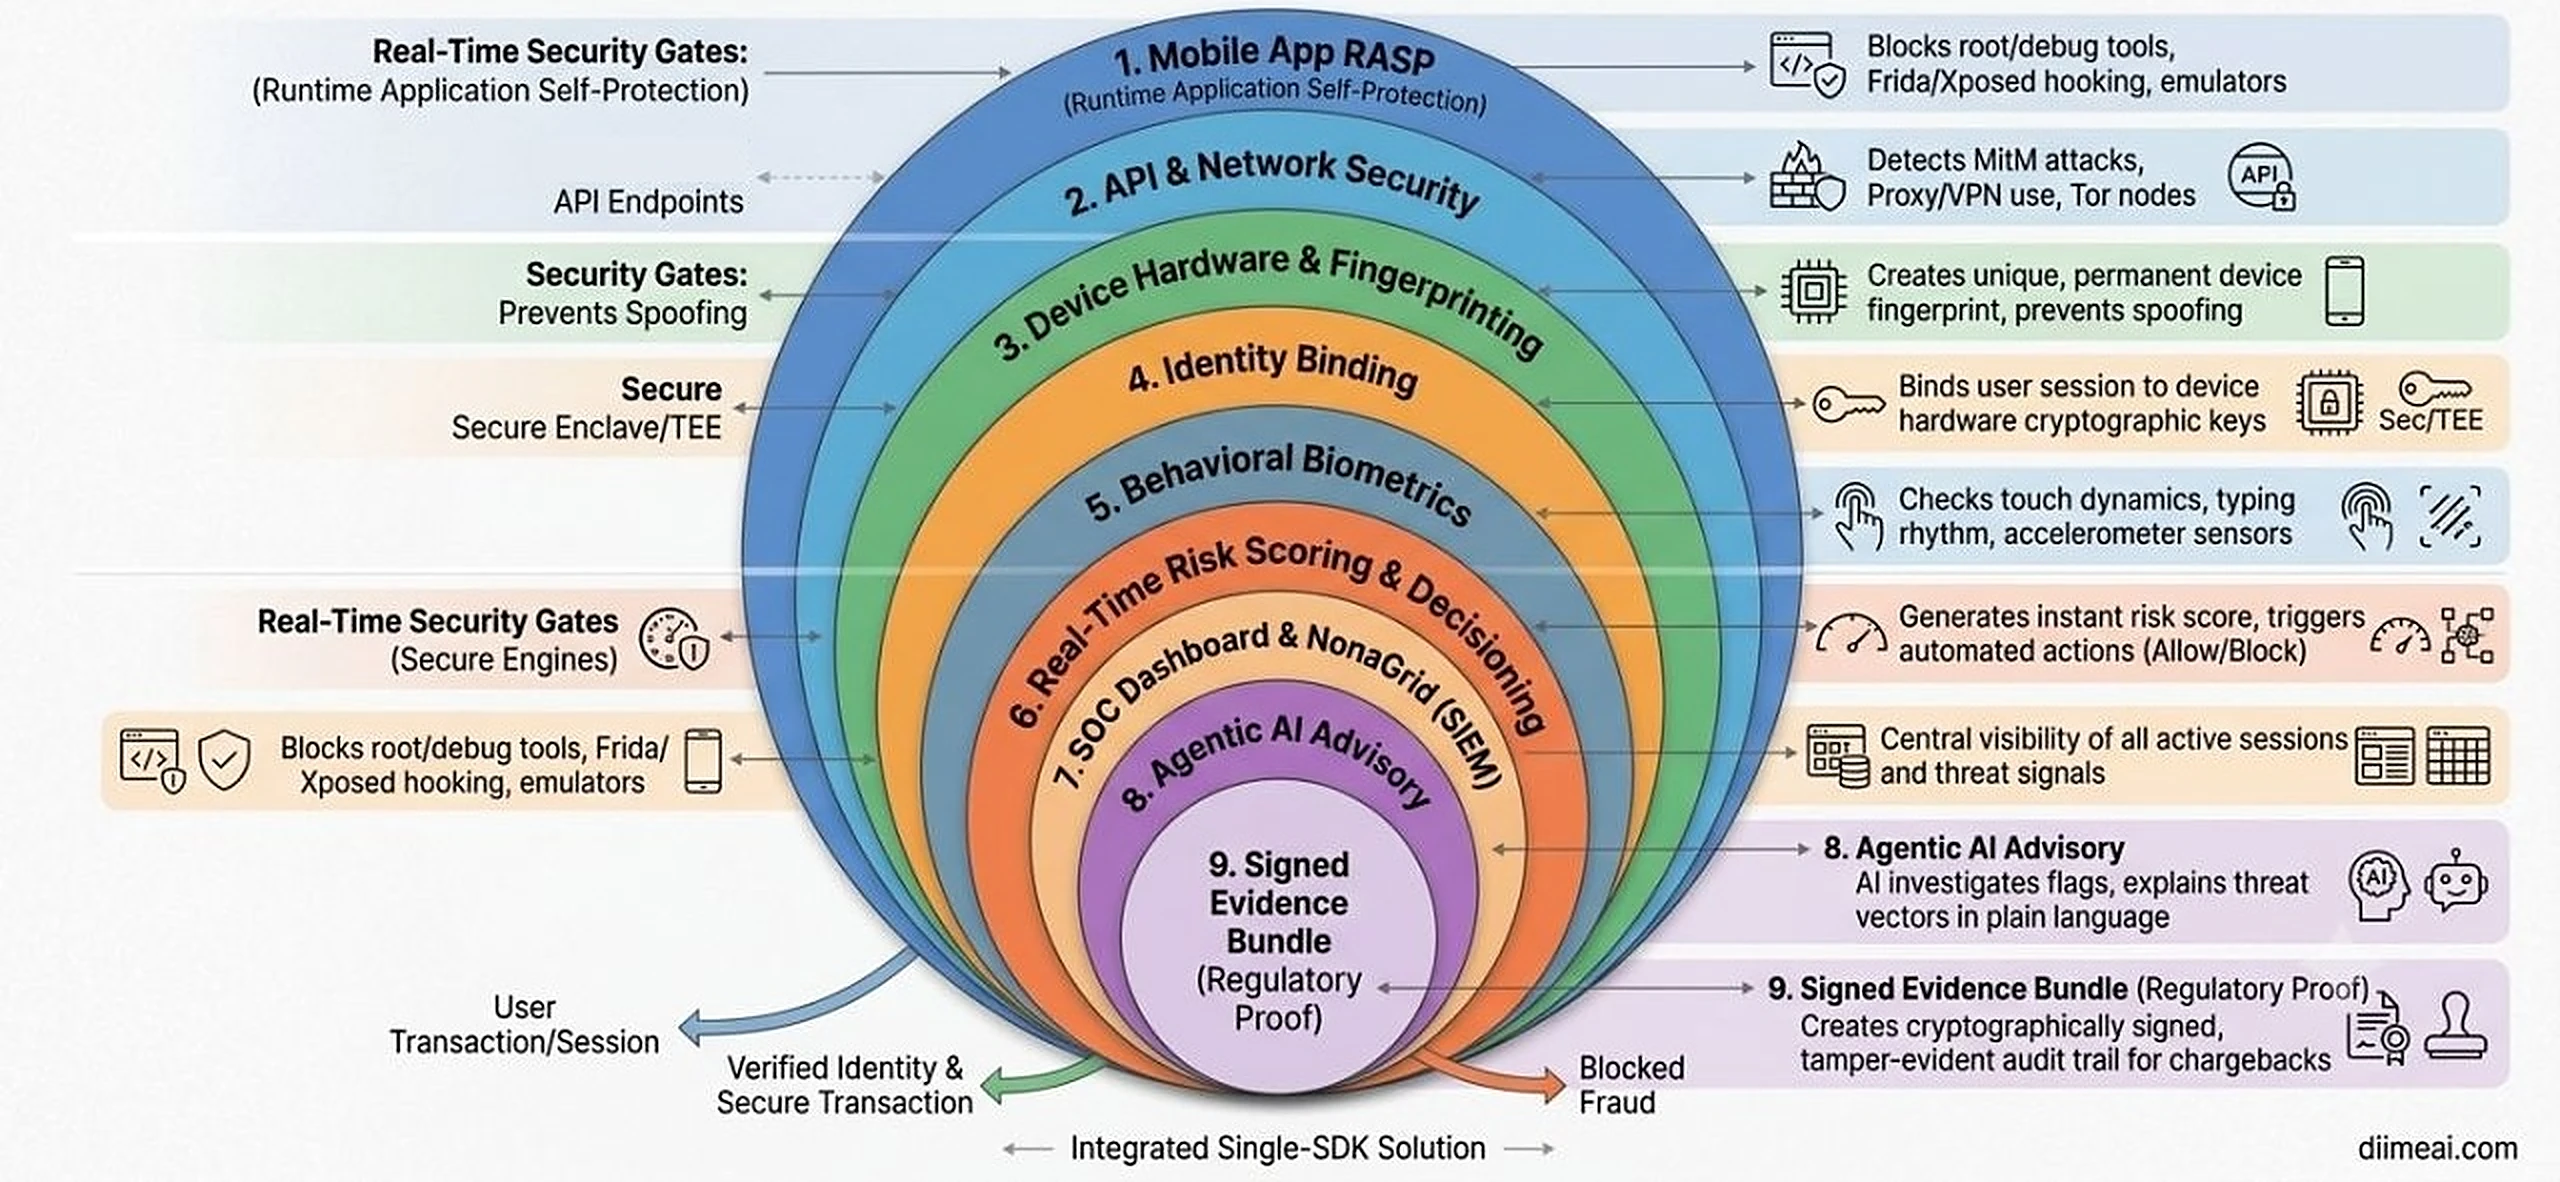
NonaShield's 9-Layer Fraud Architecture Framework
400+
Fraud Tricks Blocked
9 Layers
Total Peace of Mind
< 24h
Quick Setup
100%
Auditor Approved
The Four Gates, Layer by Layer

Nine Layers.
Scroll Through Every One.

Mobile app, device hardware, identity, behaviour, network traffic, risk decisions, an AI investigator and the dashboard that watches it all — stacked here in the order they actually work together.

Mobile App · RASP
API & Network
Device Hardware & Fingerprinting
Identity
Behaviour
Risk Scoring
SOC Dashboard · NonaGrid
Agentic AI Advisory
Signed Evidence & Compliance Mapping

Hover or tap a layer to see what it does and which fraud it helps stop. Or scroll down to walk through each layer in order.

Layer 1 of 9

Mobile App · RASP

Your App, Watched From Inside.

What it does

Continuously monitors the mobile app at runtime and detects hostile environments, instrumentation and application manipulation.

Fraud it helps stop

  • App tampering and cloning
  • Frida and Xposed hooking
  • Rooted and emulated devices
  • Remote-access and overlay abuse
Layer 2 of 9

API & Network

Every Request, Verified.

What it does

Attackers can intercept or manipulate mobile-to-API communication using MITM attacks, proxies, VPNs, Tor, replay and network manipulation. Signed-payload checks and replay protection at the edge, so a forged, altered or replayed request is rejected before it reaches your backend.

Fraud it helps stop

  • Man-in-the-middle and proxy attacks
  • Replay of old approvals
  • Forged or altered requests
Layer 3 of 9

Device Hardware & Fingerprinting

A Device That Proves Itself.

What it does

A cryptographic key that never leaves the device's secure hardware proves it's genuine and untampered — then signs every transaction it approves.

Fraud it helps stop

  • Device cloning
  • Emulator and device farms
  • Multi-account and mule accounts
Layer 4 of 9

Identity

Confirms It's Really You.

What it does

Binds the transaction to the enrolled user on their own device, so a stolen session or spoofed identity doesn't pass as the real customer.

Fraud it helps stop

  • Stolen sessions
  • Spoofed identity
  • Account takeover
Layer 5 of 9

Behaviour

Knows How You Normally Use Your Phone.

What it does

Baselines typing rhythm, motion and everyday usage patterns to catch a fraudster — or a scammer talking a real customer through a transfer.

Fraud it helps stop

  • Remote-access scams
  • A customer being coached through a transfer
  • Bots and scripted sessions
Layer 6 of 9

Risk Scoring

A Verdict, in Real Time.

What it does

Every transaction gets an instant decision — allow, step up, or block — before the money moves.

Fraud it helps stop

  • High-risk payments stopped before money moves
  • Suspicious sessions stepped up for an extra check
Layer 7 of 9

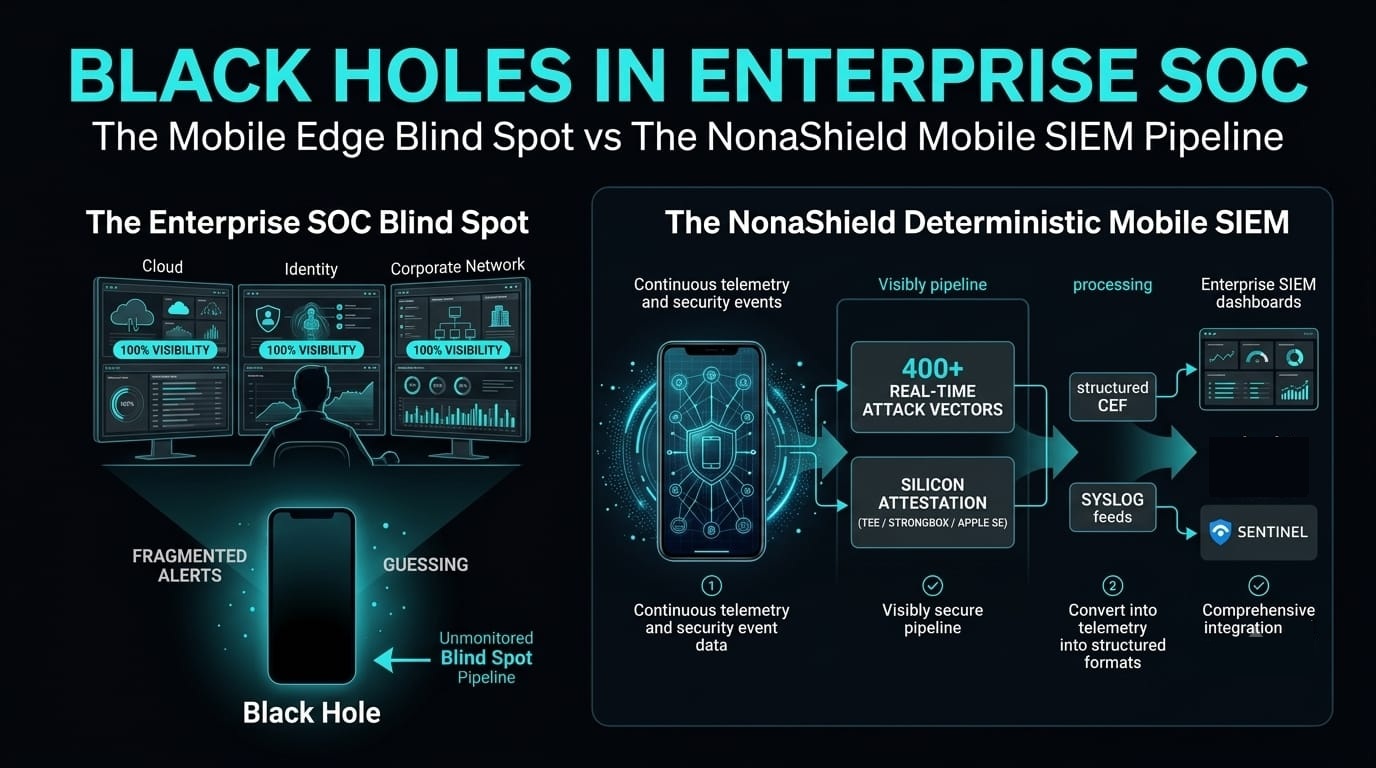
SOC Dashboard · NonaGrid

Your Own Security Command Center.

What it does

Live monitoring inside your own cloud account — one dashboard instead of stitching together a separate SIEM.

Fraud it helps stop

  • Coordinated attacks seen in one place
  • Repeated attack patterns across devices and accounts
Layer 8 of 9

Agentic AI Advisory

An Analyst for Every Case.

What it does

Investigates every flagged transaction and explains the decision in plain language — no black box, no guessing.

Fraud it helps stop

  • Helps analysts confirm real fraud faster
  • Explains why each case was flagged
Layer 9 of 9

Signed Evidence & Compliance Mapping

Create Forensically Defensible Evidence.

What it does

Creates a "cryptographically signed, tamper-evident evidence bundle" containing relevant security events, decisions, timestamps and control results. Mapped to regulatory compliance.

Fraud it helps stop

  • Disputed and repudiated transactions
  • Chargeback disputes
  • Regulator and audit requests

One Platform. Nine Layers. Every layer that can touch a transaction — app, device, identity, network, behaviour and the humans who review it — working together under one SDK, one console, one vendor.

Identity and Location

Who is it?
Where are they really?

Every transaction decision rests on two questions. Identity: is this the enrolled customer on their own device? Location: is the session where it claims to be? Fraudsters attack both, with cloned devices, stolen sessions, spoofed GPS, VPNs and proxies.

  • Identity risk
  • Location risk
Top threat origins
  • 1SingaporeVPN and proxy masking4,820
  • 2DubaiGPS spoofing4,010
  • 3LagosStolen-session account takeover3,470
  • 4São PauloDevice cloning2,890
  • 5MoscowEmulator farms2,260
  • 6LondonRemote-access scams1,740

*Sample data

Every Fraud Case Costs More
Than the Money Lost.

The money moved to one device. The controls did not move with it.

A single fraud case means hours of investigation, an upset customer, a regulator asking questions, and your team pulled off real work to piece together what happened. Multiply that by every case your app doesn't catch, and "a few fraud incidents a month" quietly becomes a full-time operational problem.

The Scale Nobody Questions
0
Mobile Banking Accounts Worldwide
0
Projected Growth of the Global Mobile Banking Market to 2033
0
Real-Time Payment Transactions Every Day in India
0
Of the World's Real-Time Payment Volume Runs Through India

Sources: Neontri, Mobile Banking Statistics 2026 (global figures are market projections) · NPCI / PIB, UPI at 10 Years, 2026.

Answer One — Is What You Already Have Enough?

The Numbers Say No.

Almost none of it is a broken phone.

0
Mobile Fraud Sessions, Year on Year
0
Rise in Text-Message Scams
The setup for almost every takeover
0
Global Online Payment Fraud Losses, Forecast for 2028
0
Recovered for Victims
Of digital payment fraud losses recovered

Sources: Juniper Research, Online Payment Fraud Losses report · BioCatch, India Digital Banking Fraud Report, Jul 2026 · Ministry of Finance, India, Rajya Sabha (Internet Banking, Credit Card and UPI fraud combined, FY22–Sep 2025).

Answer one — what you have watches the phone. The fraud never touched the phone. Every one of these happened on a handset that passed its security check.

See What Really Happened to Real People →
Critical Threats

Six mobile frauds that keep coming up.
How NonaShield stops each one.

Each threat below is matched to the layers that stop it, so you can see what protects you and where.

01

Remote-access and screen-sharing scams

The threat

A caller talks the customer into installing a remote-access app, then steers a real payment from the customer's own phone.

How NonaShield protects

Detects remote-access tools, screen mirroring and overlays on the device, and reads the session's behaviour to spot a guided customer. A risky session is stepped up or blocked before money moves.

  • Mobile RASP
  • Behaviour
  • Risk scoring
02

Account takeover and OTP theft

The threat

Stolen credentials, a hijacked session or a captured one-time password are used to log in as the real customer.

How NonaShield protects

Binds each transaction to the enrolled customer's own device with a key held in secure hardware, so a stolen session or password alone does not pass as the real customer.

  • Identity
  • Device hardware
03

Malicious apps, overlays and banking trojans

The threat

Malware watches the banking app, draws fake screens over it, or abuses accessibility services to read and tap.

How NonaShield protects

Runtime protection watches the app from the inside, detects hooking, overlays and tampering, and responds on the device before the attacker can act.

  • Mobile RASP
04

Cloned apps, emulators and device farms

The threat

One attacker runs copies of the app, or virtual phones, to create many fake users at scale.

How NonaShield protects

A hardware-attested device fingerprint recognises the same device across accounts, so one handset behind many accounts shows up as a ring instead of ten clean logins.

  • Device fingerprint
  • Hardware key
05

SIM swap and number takeover

The threat

The fraudster moves the victim's number to a new SIM to receive one-time passwords and reset access.

How NonaShield protects

A new SIM alone does not make a new device trusted. A change of device or network triggers a step-up check, and the hardware key stays with the enrolled phone.

  • Identity
  • Location
  • Risk scoring
06

AI-powered social engineering

The threat

Cloned voices, fake video calls and scripted chats make scams more convincing and let them scale.

How NonaShield protects

NonaShield cannot hear the call, but it sees the effect on the phone: remote-access tools, a hesitant, guided session, a new device or an impossible location. Those signals drive a step-up or a block.

  • Behaviour
  • Location
  • Risk scoring
That's Exactly Why We Built This

Mobile Cybersecurity,
Built Around One Job.

Add one small piece of code to your app and NonaShield does the rest. On our managed SaaS we run the backend for you, or you can deploy it in your own cloud. Together they catch fraud attempts before they succeed, on banking, lending, trading and payment apps. No new hardware. No extra steps for your customers. Just protection that's already there before the fraud starts.

Your App + one small SDK NonaShield the system behind it Verdict before money moves

Three Steps.
No New Hardware.

Add the SDK, and every session is checked before money moves. On SaaS, NonaShield runs the backend.

1

Watch

The four gates run on the device and the session — is it safe, known and proven, and is a real person driving it?

2

Decide

In real time, the system decides: let it through, ask for one more check, or stop it — before money moves.

3

Prove

Every decision is signed and recorded automatically — ready the moment anyone asks what happened.

What You Get

Four Gates.
One SDK. One Platform.

Before money moves, every session passes four checks: is the device safe, is it known, can it prove itself, and is a real person driving it. Every decision is signed as evidence.

Gate 1 · Device safe Is the phone and the app safe to trust?

Runtime app protection (RASP)

Detects and blocks root tools, Frida/Xposed hooking, emulators, debuggers, app repackaging, screen mirroring and accessibility abuse — on the phone, in real time.

RASP means the app defends itself from the inside, while it runs.

400+ fraud vectors mapped

Attack techniques across device, app, network, identity and session — each tied to a detection and a response, and kept up to date as attacks change.

Gate 2 · Device known Have we seen this device before?

Device & web fingerprint

One persistent identity for the same device or browser across mobile app and web, so reinstall, mule-account and multi-account fraud stands out.

Fraud graph & SIM-swap detection

Links devices, accounts and SIM changes across your customer base to expose fraud rings that single-account checks miss.

Gate 3 · Device proven Can the hardware itself vouch for it?

Hardware-bound identity

Secure-hardware keys (Android StrongBox / TEE, iOS Secure Enclave) tie each customer to a genuine device. The private key never leaves the hardware, so it can't be copied to another phone.

Gate 4 · Real person Is a human driving, and is it this human?

50+ behaviour signals

Touch, swipe, typing rhythm, motion sensors and session patterns build a “how this person usually acts” profile — sudden differences raise the risk.

Then The System Decides, And Proves It

Real-time risk score

Every session and transaction gets a live risk score built from all four gates — so low-risk customers glide through and risky ones stand out instantly.

Decision engine

Turns the risk score into a clear action: allow, step-up or block — your policy, your thresholds.

Signed evidence bundle

Every transaction leaves a signed, tamper-evident record of what the device, app and session looked like at that moment.

The Transaction Journey In One Line
Customer acts
opens app, starts payment
Four gates run
safe · known · proven · real person
Risk decision
allow / step-up / block
Evidence signed
stored for audit
Fits How You Run

Platforms

Android, iOS and React Native — one SDK, one managed platform.

Deployment

Our SaaS cloud, your own VPC, or fully on-premise. With the last two, your data never leaves your environment.

Compliance view

A live dashboard maps controls to RBI, NPCI, PCI DSS and DPDP requirements, and other frameworks.

See the full mapping →
Rapid Deployment Matrix

Get Live Mobile SOC in 24 Hours.

Don't spend months integrating bulky infrastructure. Our turnkey threat architecture deploys complete command, telemetry, and automated mitigation straight into your environment within a single day.

0h to 24h
Full Operational Setup
100%
Cloud Native Control
24-Hour SOC Dashboard
NonaShield SOC dashboard showing 24-hour live monitoring
Live decision streamIllustrative simulation

    Simulated events for illustration. Not customer data.

    Proof It Works at Scale
    0
    Fraud Techniques Stopped
    0
    Signals From How Someone Actually Uses Their Phone
    8% → 0%
    How Much Stolen Money Gets Recovered, With Real Evidence
    0
    Partner, Instead of Stitching Together Five Different Tools
    See It Work

    Malware Inside the App?
    RASP Catches It Live.

    Runtime Application Self-Protection watches your app from the inside while it's running, not after the fact. The moment something tries to hook into memory or slip in a malicious command, RASP sees it and blocks it before it executes — no server round-trip required.

    Explore the Platform →
    Hardware-Backed Proof

    Every Transaction Signed.
    Every Replay Rejected.

    Each transaction is sealed inside the device's Secure Enclave with a key that never leaves the hardware. Try to replay an old approval or tamper with the amount in transit, and the seal breaks instantly — the bank gateway rejects it before the money moves.

    See How Device Trust Works →
    Live in Your Browser, Right Now

    Device Trust, on Web Too.

    These cards are reading your own browser's signals live — the same device-trust checks our web agent runs, including whether this device has a real hardware-backed authenticator.

    Hello, Visitor

    Reading signals…

    Live

    Browser

    —

    Screen

    —

    Timezone

    —

    Hardware Auth

    —

    Reading signals…

    This Is Real Data

    Trust Signal

    Reading…

    Computed from the signals on the left — automation, DevTools, and hardware-authenticator checks.

    Uses your browser's own location permission — nothing is stored.

    Evidence You Can Hand
    to a Regulator.

    Every transaction gets a signed, tamper-evident record. When a customer disputes a charge, or a regulator asks for proof, you have a real answer ready — not a guess.

    It also supports India's newest data-safety law.

    DPDP Rule 6 requires reasonable security safeguards on personal data. NonaShield's evidence and access controls map to it.

    See the Full Compliance Mapping →
    Convinced? Here's Where to Look Next

    Built for Your Industry.

    14 sectors, from banking to quick commerce — each with its own fraud pattern and a brochure you can download.

    See Your Industry

    See How We Compare.

    A side-by-side look at NonaShield against other mobile fraud and device-trust vendors, sourced from their own public claims.

    View Comparison

    See It In Action.

    Live recordings of the SOC dashboard, device-cloning detection and evidence capture — the product running, not a pitch deck.

    Watch the Dashboard

    One Price Per Product.
    No Per-User Math.

    Pick what you need. Try any of them free, then decide.

    Everything Included

    NonaShield Platform

    $599
    flat, per month

    The full platform — every layer, one setup.

    Start Free Trial

    Fingerprint

    $99
    per month

    Tells a real device from a fake one — mobile and web.

    Start Free Trial

    Agentic AI Advisory

    $1,000
    per month

    An assistant that investigates every case for you.

    Start Free Trial

    NonaGrid — SIEM

    $500
    per month*

    A separate product: security monitoring inside your own environment.

    Start Free Trial

    *NonaGrid is deployed on customer premises.

    Start Your Free 7-Day Trial.

    Sign up with your company email and choose the free trial or the full platform. We'll send a verification link first. The trial needs no card.

    Direct Engineering

    jrajesh@diimeai.com

    WhatsApp Business

    +91-8591-755-427
    Choose your plan

    FAQ

    Frequently asked questions

    What is NonaShield?

    NonaShield is a mobile fraud and device-trust platform from DIMEAI. One SDK adds runtime protection, device fingerprinting, hardware-bound identity, behavioural risk scoring and signed evidence to a banking, lending, trading or payment app.

    How is NonaShield different from using separate RASP and fraud tools?

    It is one unified platform instead of several tools. Mobile RASP, device fingerprinting, identity, behaviour and risk scoring share the same signals and the same dashboard, so a decision uses everything the platform knows.

    How much does NonaShield cost?

    NonaShield is priced at a flat $599 a month, about ₹6 lakh a year, and includes RASP, fingerprinting, identity and evidence. See the pricing page for what is included.

    Which regulations does NonaShield help with?

    It helps mobile apps meet published requirements from RBI, NPCI, SEBI and DPDP, and supports PCI DSS controls for mobile payment applications. It is not an endorsement or certification by those bodies.